
Introduction
Cross-Site Scripting, commonly known as XSS, is one of the most widespread vulnerabilities affecting websites today. Unlike SQL injection, which targets a website’s database, XSS targets the trust that users place in a website by exploiting the browser itself. It allows attackers to inject malicious scripts into web pages viewed by other users, turning a legitimate, trusted website into an unwitting delivery mechanism for malware, credential theft, and other malicious activity. This article provides a thorough exploration of what XSS is, how it works, its various forms, real-world consequences, and the best practices for preventing it.
What Is Cross-Site Scripting?
Cross-Site Scripting occurs when an application includes untrusted, user-supplied data in a web page without properly validating or escaping it, allowing an attacker to inject client-side scripts — typically JavaScript — into that page. When another user visits the compromised page, their browser executes the injected script as if it were a legitimate part of the website. Because the malicious script runs within the context of the trusted website, it can access cookies, session tokens, and other sensitive information associated with that site, and it can perform actions on behalf of the victim without their knowledge.
The name “cross-site” reflects the fact that the attack often involves content from one source (the attacker) being executed in the context of another source (the trusted website), effectively crossing the boundary between the two.
How XSS Attacks Work
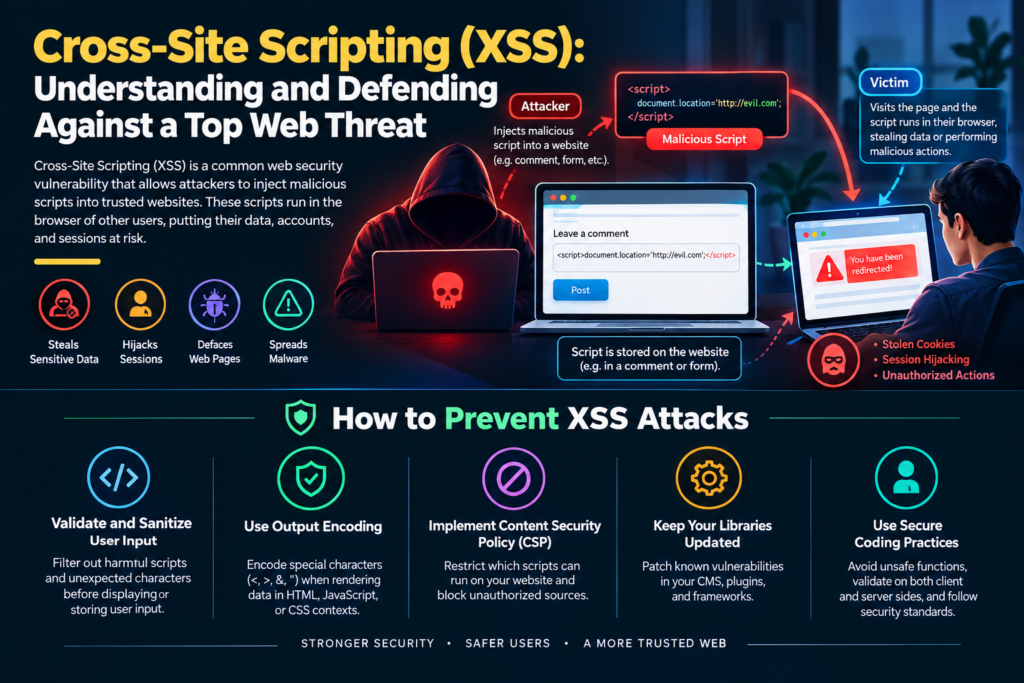
At a basic level, an XSS attack typically follows this pattern: an attacker identifies a part of a website that accepts user input and later displays that input back to other users without properly sanitizing it — this could be a comment section, a search box, a user profile field, or a URL parameter. The attacker crafts input containing malicious JavaScript code instead of normal text. When the application later renders this input as part of a web page without proper encoding, the browser interprets the injected code as legitimate script and executes it.
Once executed, this script can perform a wide range of malicious actions: stealing session cookies to hijack a user’s authenticated session, redirecting users to phishing pages designed to steal credentials, modifying the content of the page (defacement), logging keystrokes, or even using the victim’s browser to perform actions on other websites where they are logged in.
Types of XSS Attacks
1. Stored XSS (Persistent XSS)
Stored XSS is considered the most dangerous variant because the malicious script is permanently saved on the target server — for example, in a database, comment field, forum post, or user profile — and is then served to every user who views the affected page. This means the attack does not require tricking a specific victim into clicking a malicious link; simply visiting the affected page is enough to trigger the attack. Because it can affect a large number of users automatically, stored XSS is particularly valuable to attackers seeking widespread impact.
2. Reflected XSS
Reflected XSS occurs when malicious script is included as part of a request (commonly in a URL parameter or form submission) and is immediately reflected back in the server’s response without being stored. This type of attack typically requires social engineering, as the attacker must trick the victim into clicking a specially crafted link — often distributed through phishing emails, malicious advertisements, or fake websites. Because the payload is not stored, each attack attempt must individually target a victim.
3. DOM-Based XSS
DOM-based XSS is a variant where the vulnerability exists entirely within client-side code rather than in how the server processes and returns data. In this case, a website’s own JavaScript takes data from an untrusted source (such as the URL) and passes it to a function that can dynamically update the page content in an unsafe way, without the data ever being sent to the server. Because the entire attack occurs within the browser’s Document Object Model (DOM), it can be more difficult to detect through traditional server-side security scanning.
Real-World Consequences of XSS
The impact of a successful XSS attack can range from minor annoyance to severe security compromise, depending on what the attacker chooses to do with their access:
- Session hijacking: By stealing session cookies, attackers can impersonate legitimate users without needing their passwords, gaining full access to their accounts.
- Credential theft: Attackers can inject fake login forms that appear identical to the real website, capturing usernames and passwords as users unknowingly submit them.
- Malware distribution: Injected scripts can redirect visitors to malicious websites that attempt to install malware on their devices.
- Website defacement: Attackers can alter the visual appearance or content of a website, damaging the organization’s reputation.
- Data theft: Scripts can be used to exfiltrate any information accessible within the page, including personal data displayed to authenticated users.
- Propagation of worms: On platforms with social features, particularly social media sites, XSS vulnerabilities have historically been used to create self-propagating worms that spread automatically between users.
How to Prevent Cross-Site Scripting
Preventing XSS requires a combination of secure coding practices, proper use of modern web frameworks, and defense-in-depth security measures.
1. Output Encoding
The single most important defense against XSS is proper output encoding, also known as output escaping. This means that whenever user-supplied data is included in a web page, it must be encoded appropriately for the specific context in which it appears — HTML body content, HTML attributes, JavaScript, CSS, or URLs each require different encoding rules. Proper encoding ensures that special characters (such as angle brackets used to define HTML tags) are displayed as literal text rather than being interpreted as executable code or markup by the browser.
2. Input Validation
While output encoding is the primary defense, validating input on the server side provides an important additional layer of protection. Input validation should follow an allow-list approach, defining exactly what characters, formats, and lengths are acceptable for each specific field, rather than attempting to block known malicious patterns, which attackers can often find ways to bypass.
3. Use Modern Frameworks with Built-In Protections
Modern front-end frameworks such as React, Angular, and Vue automatically escape content by default when rendering data into the DOM, significantly reducing the risk of XSS compared to manually constructing HTML strings. However, developers must remain cautious, as these frameworks typically provide mechanisms to bypass this automatic escaping for cases where raw HTML rendering is genuinely needed — such functions should be used sparingly and only with thoroughly sanitized content.
4. Content Security Policy (CSP)
A Content Security Policy is a browser security feature that allows website administrators to specify which sources of content — scripts, styles, images, and other resources — are allowed to load and execute on a given page. By restricting script execution to trusted sources only, a well-configured CSP can prevent injected scripts from executing even if an XSS vulnerability exists elsewhere in the application, serving as a powerful additional layer of defense.
5. HttpOnly and Secure Cookie Flags
Setting the HttpOnly flag on sensitive cookies, such as session identifiers, prevents client-side JavaScript from accessing those cookies entirely. This means that even if an attacker successfully injects a script through an XSS vulnerability, they cannot steal the session cookie directly through that script. Combining this with the Secure flag, which ensures cookies are only transmitted over encrypted HTTPS connections, further strengthens cookie security.
6. Sanitize Rich Text Input Carefully
Applications that need to allow users to submit formatted content, such as blog comments with basic formatting or rich text editors, face a particular challenge since they cannot simply encode all HTML. In these cases, a well-tested HTML sanitization library should be used to strip out potentially dangerous elements and attributes (such as script tags and event handlers) while preserving safe formatting elements.
7. Avoid Dangerous JavaScript Functions
Certain JavaScript functions and DOM properties are particularly prone to enabling DOM-based XSS when used carelessly with untrusted data, such as directly injecting content into a page in a way that gets interpreted as executable code. Developers should favor safer alternatives that treat inserted content strictly as text rather than executable markup whenever the content includes any untrusted data.
8. Regular Security Testing
As with other web vulnerabilities, regular security testing — including automated scanning tools, manual code review, and penetration testing — helps identify XSS vulnerabilities before they can be exploited. Browser extensions and automated tools specifically designed to detect XSS vulnerabilities can be integrated into development and testing workflows.
9. Keep Dependencies Updated
Third-party libraries and frameworks used in a website’s front end and back end are regularly updated to patch known XSS vulnerabilities. Maintaining an up-to-date technology stack, including all JavaScript libraries and plugins, is essential for closing known security gaps.
The Role of Browsers in XSS Defense
Modern web browsers have also implemented various built-in protections against XSS over the years, although developers should never rely solely on browser-level protections as their primary defense, since these mechanisms can have limitations and are not consistently implemented across all browsers. Instead, browser protections should be viewed as one additional layer within a broader, defense-in-depth security strategy.
Conclusion
Cross-Site Scripting remains one of the most common and consequential vulnerabilities affecting websites, precisely because it exploits the fundamental trust relationship between users and the websites they visit. Because modern websites are increasingly interactive and dynamic, involving extensive use of user-generated content, the potential surface area for XSS vulnerabilities continues to grow. However, by consistently applying proper output encoding, leveraging the built-in protections of modern frameworks, implementing a strong Content Security Policy, and maintaining rigorous security testing practices, organizations can significantly reduce their exposure to this pervasive threat.
In the next installment of this series, we turn our attention to a different category of threat entirely: Distributed Denial of Service (DDoS) attacks, which aim not to steal data but to overwhelm and disable a website’s availability altogether.